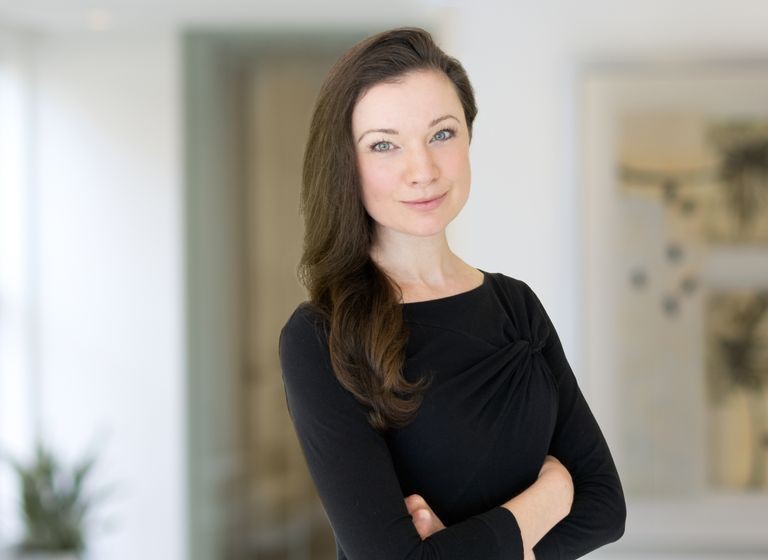
Kate M. GrowleyCIPP/G/US, AIGP, CMMC RP
Overview
|
Businesses around the globe rely on Kate M. Growley to navigate their most challenging digital issues, particularly those involving cybersecurity, artificial intelligence, digital infrastructure, and their intersection with national security. Clients seek her guidance on proactive compliance, incident response, internal and government-facing investigations, and policy engagement. With a unique combination of legal, policy, and consulting experience, Kate excels in translating complex technical topics into advice that is practical and informed by risk and business needs. |  |
Career & Education
- Florida State University, B.S., summa cum laude, International Relations
- University of Virginia School of Law, J.D.
- Virginia
- District of Columbia
Kate's Insights
Client Alert | 4 min read | 09.21.26
In a First, District Court Dismisses FCA Cybersecurity Complaint for Lack of Materiality
In recent years, the U.S. federal government has taken significant interest in the cybersecurity compliance of its contractor base. In 2025 alone, the U.S. Department of Justice’s (DOJ) Civil Cyber-Fraud Initiative recovered more than $50 million across nine False Claims Act (FCA) cybersecurity fraud settlements, and it has secured almost 20 settlements since its launch in October 2021. Because most defendants facing FCA liability for alleged cybersecurity noncompliance enter into pre-litigation settlements, the last court decision in a cybersecurity FCA case was in 2022. However, earlier this month, on September 2, 2026, in United States ex rel. Pannek v. Archer Daniels Midland Co., No. 23-cv-15145, 2026 WL 2593317 (N.D. Ill. Sept. 2, 2026), Judge Sunil R. Harjani of the U.S. District Court for the Northern District of Illinois granted a motion to dismiss on materiality grounds and offered additional guidance on what a plaintiff must allege to adequately state an FCA cybersecurity claim.
Speaking Engagement | 09.16.26
“Information Risk Management,” 4th Annual Midwest Government Contracts Seminar, Chicago, IL
Press Coverage | 09.11.26
Press Coverage | 09.11.26
Cyberattack causes a flight delay? Airlines won’t owe you a hotel or meal
Insights
- |
08.01.25
Journal of Federal Agency Action
Global Developments: New Actions in the Asia-Pacific
|05.14.24
Privacy and Cybersecurity Outlook: The 2024 Landscape
China: Recent Developments In Cross-Border Data Transfer Requirements
|12.18.23
OneTrust DataGuidance
Cybersecurity Provisions Proliferate In The National Defense Authorization Act
|03.15.22
Government Contracting Law Report
Advancing America’s Dominance in AI: The 2021 National Defense Authorization Act’s AI Developments
|05.06.21
The Journal of Robotics, Artificial Intelligence & Law
- |
04.27.21
Government Contracting Law Report
"Supply Chain Under Siege: Strategic Defense in a Regulated World," RSAC 2026
|03.26.26
"Privacy Frameworks in the United States and Asia", AI and Data Privacy
|11.12.25
CMMC Review: DoD’s Inconsistent Cui Marking Continues To Plague Program
|08.19.26
Federal News Network
Department of War Immediately Suspends CMMC Phase II Requirements, Launches 60-Day Reform Review
|07.22.26
Crowell & Moring's Government Contracts Legal Forum
Special Edition of the Fastest 5 Minutes: Suspension of CMMC Phase II Requirements
|07.22.26
Crowell & Moring's Government Contracts Legal Forum
Logged Out: How LOGZONE’s DIBCAC Challenges Put It Squarely in DOJ’s Crosshairs
|07.13.26
Crowell & Moring's Government Contracts Legal Forum
Time for a Change: FedRAMP Fundamentally Revamps Program With Consolidated Rules for 2026
|07.13.26
Crowell & Moring's Government Contracts Legal Forum
White House National AI Policy Framework Calls for Preempting State Laws, Protecting Children
|04.25.26
Crowell & Moring’s Retail & Consumer Products Law Observer
FedRAMP Solicits Public Comment on Overhaul to Incident Communications Procedures
|04.22.26
Crowell & Moring’s Government Contracts Legal Forum
AI for Government: 7 Days for Contractor Comments on GSA Proposed Contract Clause for AI Systems
|03.16.26
Crowell & Moring’s Government Contracts Legal Forum
DHS Announces Virtual Town Halls on CIRCIA Final Rule
|02.20.26
Crowell & Moring’s Government Contracts Legal Forum
FedRAMP Proposes Updates to Authorization Process—Six New RFCs Released for Public Comment
|01.26.26
Crowell & Moring’s Government Contracts Legal Forum
FedRAMP Proposes Updates to Authorization Process—Six New RFCs Released for Public Comment
|01.22.26
Crowell & Moring’s Government Contracts Legal Forum
Kate's Insights
Client Alert | 4 min read | 09.21.26
In a First, District Court Dismisses FCA Cybersecurity Complaint for Lack of Materiality
In recent years, the U.S. federal government has taken significant interest in the cybersecurity compliance of its contractor base. In 2025 alone, the U.S. Department of Justice’s (DOJ) Civil Cyber-Fraud Initiative recovered more than $50 million across nine False Claims Act (FCA) cybersecurity fraud settlements, and it has secured almost 20 settlements since its launch in October 2021. Because most defendants facing FCA liability for alleged cybersecurity noncompliance enter into pre-litigation settlements, the last court decision in a cybersecurity FCA case was in 2022. However, earlier this month, on September 2, 2026, in United States ex rel. Pannek v. Archer Daniels Midland Co., No. 23-cv-15145, 2026 WL 2593317 (N.D. Ill. Sept. 2, 2026), Judge Sunil R. Harjani of the U.S. District Court for the Northern District of Illinois granted a motion to dismiss on materiality grounds and offered additional guidance on what a plaintiff must allege to adequately state an FCA cybersecurity claim.
Speaking Engagement | 09.16.26
“Information Risk Management,” 4th Annual Midwest Government Contracts Seminar, Chicago, IL
Press Coverage | 09.11.26
Press Coverage | 09.11.26
Cyberattack causes a flight delay? Airlines won’t owe you a hotel or meal
