
Thanasis Christou
Overview
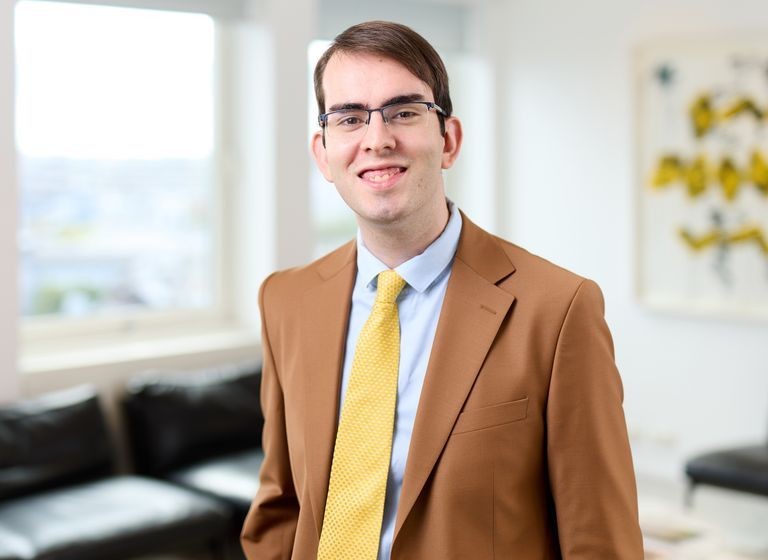
Thanasis Christou is an associate with Crowell & Moring’s Privacy & Cybersecurity Group. Based in Brussels, he focuses his practice on the intersection of privacy, cybersecurity, and broader EU technology law. He advises clients on strategic cross-border incident response and regulatory enforcement matters. He also assists clients on the implementation of the GDPR, the EU AI Act, the NIS2 Directive and the Cyber Resilience Act (CRA), and he provides general counseling services in relation to all aspects of EU Digital Regulation law.
Career & Education
- University of California, Berkeley School of Law, LL.M., Certificate of Specialization in Law and Technology, 2025
- National Kapodistrian University of Athens, LL.B., summa cum laude, 2022
- Greece/EU
- California
- Certified Information Privacy Professional Europe (CIPP/E), IAPP
- Certified Information Privacy Professional United States (CIPP/US), IAPP
- Member of the American Bar Association’s Science and Technology Section (2024–2026)
- Member of the Copyright Society
- English
- French
- Greek
Thanasis's Insights
Client Alert | 5 min read | 10.19.26
To Fine or Not to Fine: EDPB Confirms Default Position in GDPR Enforcement Should Be to Fine
On 17 September 2026, the European Data Protection Board (“EDPB”) published its draft Guidelines 04/2026 on the imposition of administrative fines (the "Guidelines"), currently out for public consultation until 13 November 2026. In 2022, the EDPB had adopted guidelines on calculating the amount of an administrative fine (the “Calculation Guidelines”). The present Guidelines fill a gap the Calculation Guidelines left open: they provide a structured, five-step methodology for deciding when to impose a fine and explain how fines interact with the full range of corrective powers. By issuing both sets of guidelines, the EDPB aims to increase harmonization in fining posture.
Client Alert | 6 min read | 09.11.26
It’s LIVE: The Cyber Resilience Act Reporting Is Mandatory as of Today - 11 September 2026
Representative Matters
- Representing one of the world’s leading B2B and B2G mission-critical communications and security solutions provider in a global cyber incident impacting 200+ jurisdictions;
- Counselling a global enterprise HR software solutions provider in relation to the implementation of new AI deployments in relation to its global workforce under the EU AI Act;
- Providing product and compliance counsel to a prominent video management software company under the EU Cyber Resilience Act (CRA);
- Assisting a U.S. airline with sensitive GDPR DSARs and related information requests, biometric processing restrictions and Global Privacy Controls (GPC);
- Representing a leading global industrial automation and digital transformation company in complex CRA implementation projects;
- Counselling various clients in critical infrastructure in assessing biometric verification and authentication restrictions under GDPR and U.S. State law regimes;
- Advising a leading retailer in relation to matters under the EU Data Act;
- Advising an energy tech provider on international data transfers in the context of US litigation and e-discovery requests.
Thanasis's Insights
Client Alert | 5 min read | 10.19.26
To Fine or Not to Fine: EDPB Confirms Default Position in GDPR Enforcement Should Be to Fine
On 17 September 2026, the European Data Protection Board (“EDPB”) published its draft Guidelines 04/2026 on the imposition of administrative fines (the "Guidelines"), currently out for public consultation until 13 November 2026. In 2022, the EDPB had adopted guidelines on calculating the amount of an administrative fine (the “Calculation Guidelines”). The present Guidelines fill a gap the Calculation Guidelines left open: they provide a structured, five-step methodology for deciding when to impose a fine and explain how fines interact with the full range of corrective powers. By issuing both sets of guidelines, the EDPB aims to increase harmonization in fining posture.
Client Alert | 6 min read | 09.11.26
It’s LIVE: The Cyber Resilience Act Reporting Is Mandatory as of Today - 11 September 2026
Insights
Practices
- Privacy and Cybersecurity
- Privacy and Cybersecurity Investigations
- Incident Response
- Ransomware
- Artificial Intelligence
- Cross-Border Data Flows
- Privacy and Cybersecurity — Brussels Practice
- European General Data Protection Regulation (GDPR)
- European General Data Protection Regulation (GDPR) — Brussels Practice
Thanasis's Insights
Client Alert | 5 min read | 10.19.26
To Fine or Not to Fine: EDPB Confirms Default Position in GDPR Enforcement Should Be to Fine
On 17 September 2026, the European Data Protection Board (“EDPB”) published its draft Guidelines 04/2026 on the imposition of administrative fines (the "Guidelines"), currently out for public consultation until 13 November 2026. In 2022, the EDPB had adopted guidelines on calculating the amount of an administrative fine (the “Calculation Guidelines”). The present Guidelines fill a gap the Calculation Guidelines left open: they provide a structured, five-step methodology for deciding when to impose a fine and explain how fines interact with the full range of corrective powers. By issuing both sets of guidelines, the EDPB aims to increase harmonization in fining posture.
Client Alert | 6 min read | 09.11.26
It’s LIVE: The Cyber Resilience Act Reporting Is Mandatory as of Today - 11 September 2026
